
- BỘ PHÁT WIFI
- THIẾT BỊ CHIA MẠNG SWITCH
- BỘ ĐỊNH TUYẾN ROUTER
- THIẾT BỊ TƯỜNG LỬA FIREWALL
- MÁY CHỦ (SERVER)
- BỘ LƯU TRỮ - Storage
- BỘ LƯU ĐIỆN UPS








- Quay về
- Xem tất cả "BỘ PHÁT WIFI"
- -Cisco Wi-Fi
- -Ruckus Wi-Fi
- -Ruijie Wi-Fi
- -Grandstream Wi-Fi
- -Aruba Wi-Fi
- -Alcatel Wi-Fi
- -Unifi Wi-Fi
- -Huawei Wi-Fi
- -H3C Wi-Fi
- -Juniper Wi-Fi
- Quay về
- Xem tất cả "THIẾT BỊ CHIA MẠNG SWITCH"
- -Cisco Switches
- -Fortinet Switches
- -H3C Switches
- -HPE Aruba Switches
- -Alcatel-Lucent Switches
- -Ruijie Switches
- -Mikrotik Switches
- -Juniper Switch
- Quay về
- Xem tất cả "BỘ ĐỊNH TUYẾN ROUTER"
- -Router Mikrotik
- -Router H3C series
- -UBNT Router
- -Router Cisco
- -Router Linksys
- -Router Peplink Balance


RG-S6510-4C 100GE Data Center Access Switch
Mã sản phẩm: RG-S6510-4C Tình trạng: Còn hàng Thương hiệu: Ruijie- Số khe cắm module: 4 khe cắm linh hoạt.
- Dung lượng chuyển mạch: 6.4 Tbps.
- Tốc độ chuyển tiếp: 2.000 Mpps.
- Bộ nhớ MAC: 96K địa chỉ.
- Hỗ trợ VLAN: 4K VLAN.
- Kích thước: 442 mm x 620 mm x 44 mm.
- Nguồn điện: Hỗ trợ nguồn dự phòng AC/DC.
- Hệ điều hành: Ruijie RGOS với CLI, SNMP, Web GUI, Telnet, SSH
 Sản Phẩm Chính Hãng 100% Đầy Đủ CO/CQ
 Giá Cạnh Tranh Rẻ Nhất Thị Trường
 Giao Hàng Trên Toàn Quốc
 Hỗ Trợ Kỹ Thuật Chuyên Nghiệp, Nhiệt Tình
 Ưu Đãi Lớn Cho Đại Lý Và Dự Án
 Chăm Sóc Khách Hàng Trước, Trong và Sau Khi Mua Hàng Tận Tâm.
THƯỜNG ĐƯỢC MUA CÙNG
Mô tả sản phẩm
Tổng quan về dòng RG-S6510
Thiết bị chuyển mạch dòng RG-S6510 là thiết bị chuyển mạch thế hệ mới được Ruijie Networks phát hành dành cho các trung tâm dữ liệu đám mây và khuôn viên cao cấp. Chúng nổi bật nhờ hiệu suất cao, mật độ cao và tốc độ dữ liệu lên tới 25 Gbps/100 Gbps. Chúng đáp ứng các yêu cầu thiết kế kiến trúc mạng Spine-Leaf
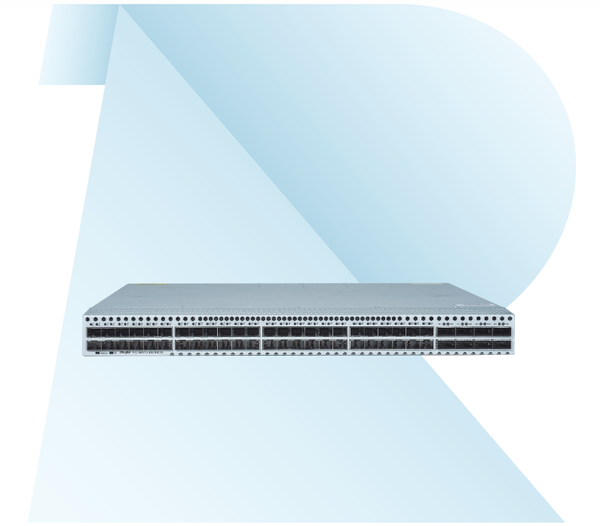
Ruijie RG-S6510-4C – Switch Core Modular Hiệu Suất Cao
Ruijie RG-S6510-4C là dòng switch core linh hoạt với 4 khe cắm module, cho phép mở rộng hệ thống với các giao diện tốc độ cao như 100GbE, 40GbE, 25GbE và 10GbE. Với dung lượng chuyển mạch lên đến 6.4 Tbps và tốc độ chuyển tiếp 2.000 Mpps, thiết bị đảm bảo hiệu suất mạnh mẽ, đáp ứng nhu cầu truyền tải dữ liệu lớn của các doanh nghiệp và trung tâm dữ liệu.
Hỗ trợ công nghệ ảo hóa VSU, RG-S6510-4C cho phép kết nối nhiều switch thành một hệ thống thống nhất, giúp đơn giản hóa quản lý và tăng cường tính dự phòng. Các tính năng bảo mật tiên tiến như chống tấn công DoS, kiểm soát ARP, xác thực 802.1X và ACL phần cứng giúp bảo vệ hệ thống mạng khỏi các mối đe dọa an ninh.

Thiết kế 1U rackmount (442 mm x 620 mm x 44 mm), hỗ trợ nguồn dự phòng AC/DC và quạt làm mát thay thế nóng, giúp đảm bảo hệ thống vận hành liên tục, ổn định. RG-S6510-4C là lựa chọn lý tưởng cho các doanh nghiệp cần một giải pháp mạng modular mạnh mẽ, linh hoạt và bảo mật cao.
Thông số kĩ thuật
System Specifications | RG-S6510-4C |
Ports | 25GE, 40GE, and 100GE ports |
Slots | 4 |
Expansion Modules | M6500-24VS2CQ, M6500-08CQ, M6500-16QXS |
Expansion Module Slots | Power supply module slots Fan module slots |
Management Port | One management port, one console port, and one USB port, compliant with the USB2.0 standard |
Switching Capacity | 6.4 Tbps |
Packet Forwarding Rate | 2030 Mpps |
802.1Q VLAN | 4094 |
Dimensions and Weight | |
Dimensions | 442 mm x 520 mm x 86 mm (17.40 in. x 20.47 in. x 3.39 in., 2 RU) |
Weight | About 14 kg (30.86 lbs., including power supply modules and fan modules) |
Power Supply and Consumption | |
AC | Rated voltage: 110 V/220 V Rated voltage range: 100 V AC to 240 V AC, 50 Hz to 60 Hz Maximum voltage range: 90 V AC to 264 V AC, 47 Hz to 63 Hz Rated input current: 5 A to 10 A |
High-voltage DC | RG-PA800I-F module ● HVDC voltage range: 180 V DC to 310 V DC ● Rated voltage: 240 V DC ● Max input current: 5 A RG-PD800I-F module ● Rated voltage range: –36 V DC to –72 V DC ● Rated voltage: –48V DC ● Max input current: 23 A |
Maximum Power Consumption | ● Max: 650 W ● Typical: 455 W ● Static: 202 W |
Environment and Reliability | |
Operating Temperature | 0ºC to 40ºC (32ºF to 104ºF) |
Storage temperature | -40 °C to 70 °C (-40 °F to 158 °F) |
Operating Humidity | 10% RH to 90% RH (Non-condensing) |
Storage humidity | 5% to 95% RH (non-condensing) |
Working altitude | Operating altitude: up to 5000 m (16,404.20 ft.) Storage altitude: up to 5000 m (16,404.20 ft.) |
Software Specifications
Software Specifications | RG-S6510-4C |
Device virtualization | Virtual Switching Unit 3.0 |
L2 Protocols | IEEE802.3ad (Link Aggregation Control Protocol), IEEE802.1p, IEEE802.1Q, IEEE802.1D (STP), IEEE802.1w (RSTP), IEEE802.1s (MSTP), IGMP Snooping, MLD Snooping, Jumbo Frame (9 KB), IEEE802.1ad (QinQ and selective QinQ), GVRP |
L3 Protocols (IPv4) | BGP4, OSPFv2, RIPv1, RIPv2, MBGP, LPM Routing, Policy-based Routing (PBR), Route-policy, Equal-Cost Multi-Path Routing (ECMP), WCMP, VRRP, IGMP v1/v2/v3, PIM-SSM/SM/DM, MSDP, Any-RP |
IPv6 Basic Protocols | Neighbor Discovery, ICMPv6, Path MTU Discovery, DNSv6, DHCPv6, ICMPv6, ICMPv6 redirection, ACLv6, TCP/UDP for IPv6, SNMP v6, Ping/Traceroute v6, IPv6 RADIUS, Telnet/SSH v6, FTP/TFTP v6, NTP v6, IPv6 MIB support for SNMP, VRRP for IPv6, IPv6 QoS |
IPv6 Features | Static routing, ECMP, PBR, OSPFv3, RIPng, BGP4+, MLDv1/v2, PIM-SMv6, manual tunnel, automatic tunnel, IPv4 over IPv6 tunnel, and ISATAP tunnel |
Data Center Features | VXLAN routing and VXLAN bridging EVPN VXLAN IPv6 VXLAN over IPv4 PFC, ECN, and other data center features RDMA M-LAG OpenFlow 1.3 |
Visualization | gRPC sFLOW sampling INT |
ACL | Standard IP-based ACL、Extended MAC-based ACL、Extended IP-bsaed ACL、Expert-level ACL、ACL 80、IPv6 ACL、ACL Logging、Ingress/Egress ACLs、ACL Counter (Ingress and egress counters are supported in interface or global configuration modes)、ACL Re-marking、Global ACL、ACL-based Redirection、Displaying ACL Resources、Processing First Packet of TCP Handshake When Binding the ACL to Restrict SIP、Matching Against 5-Tuple of Pass-by VXLAN Inner IP Packets、The expert-level ACL supports matching the IP flag and DSCP fields of VXLAN inner packets |
QoS | Mapping of IEEE 802.1p, DSCP, and ToS priorities |
Virtualization | Virtual Switching Unit |
Buffer Management | Buffer status monitoring and management, and identification of burst traffic |
HA Design | GR for RIP/OSPF/BGP, BFD, REUP dual-link fast switching and RLDP unidirectional link detection, 1+1 power redundancy, and fan redundancy, and hot swapping for all cards and power supply modules |
Security Features | Network Foundation Protection Policy (NFPP), CPP, DDoS attack defense, illegitimate data packet detection, data encryption, source IP spoofing prevention, IP scanning prevention, RADIUS/TACACS, IPv4/v6 packet filtering by basic ACL, extended ACL or VLAN-based ACL, plaintext-based and MD5 ciphertext-based authentication for OSPF, RIPv2, and BGPv4 packets, telnet login and password mechanisms for restricted IP addresses, uRPF, broadcast packet suppression, DHCP Snooping, gateway ARP spoofing prevention, and ARP check |
Management Mode | SNMP v1/v2c/v3, Netconf, telnet, console, MGMT, RMON, SSHv1/v2, FTP/TFTP, NTP clock, Syslog, SPAN/RSPAN, Telemetry, ZTP, Python, fan and power supply alarm, and temperature alarm |
Other Protocols | DHCP Client, DHCP Relay, DHCP Server, DNS Client, UDP relay, ARP Proxy, and Syslog |
Safety and Regulatory Compliance
Specification | RG-S6510-4C |
Safety | ● NM EN 62368-1 ● NM CEI62368-1 ● IEC 62368-1 ● EN 62368-1 ● BS EN 62368-1 ● UL 62368-1 ● CSA C22.2#62368-1 ● GB 4943.1 |
Electromagnetic Compatibility (EMC) | ● EN 61000-4-2 ● EN 61000-4-3 ● EN 61000-4-4 ● EN 61000-4-5 ● EN 61000-4-6 ● EN 61000-4-11 ● EN 55032 ● EN 55035 ● EN 61000-3-2 ● EN 61000-3-3 ● EN IEC 61000-3-2 ● EN IEC 61000-3-3 ● EN 300 386 ● ETSI EN 300 386 ● NM EN 55035 ● NM EN 61000-3-2 ● NM EN 61000-3-3 ● BS EN 55032 ● BS EN 55035 ● BS EN 61000-3-2 ● BS EN 61000-3-3 ● CNS 13438 ● FCC CFR Title 47, Part 15, Subpart B ● ANSI C63.4-2014 ● ICES-003 Issue 7 ● GB/T 9254.1 |
Environment | ● 2011/65/EU EN 50581 ● 2012/19/EU EN 50419 ● (EC) No.1907/2006 ● GB/T 26572 |


